Level 2
Apr 24, 2022 6:14 AM UTC
Solved

Invalid SAML token - AEM 6.5.8

I am trying to setup a new ec2 instance, and on author instance. The SAML Authentication is failing and throwing the below error.


 com.adobe.granite.auth.saml.SamlAuthenticationHandler Login failed. SAML token invalid.
 com.adobe.granite.auth.saml.SamlAuthenticationHandler SAML error with reason: invalid_token detected, redirect user to: /libs/granite/core/content/login.error.html?j_reason=invalid_token
 *INFO* [qtp1714949751-38787] org.apache.sling.auth.core.impl.SlingAuthenticator getAnonymousResolver: Anonymous access not allowed by configuration - requesting credentials
 *INFO* [qtp1714949751-38787] org.apache.sling.auth.core.impl.SlingAuthenticator getAnonymousResolver: Anonymous access not allowed by configuration - requesting credentials
 *WARN* [qtp1714949751-38787] org.apache.sling.auth.core.AuthUtil isRedirectValid: Redirect target must not be empty or null
 *ERROR* [qtp1714949751-43800] org.apache.sling.auth.core.impl.SlingAuthenticator doLogin: Cannot login: Response already committed


 I was able to setup the SAML authentication on Dev environment. On QA I did the same(The configs are updated accordingly). But getting the above issue. Can someone help me on this issue?
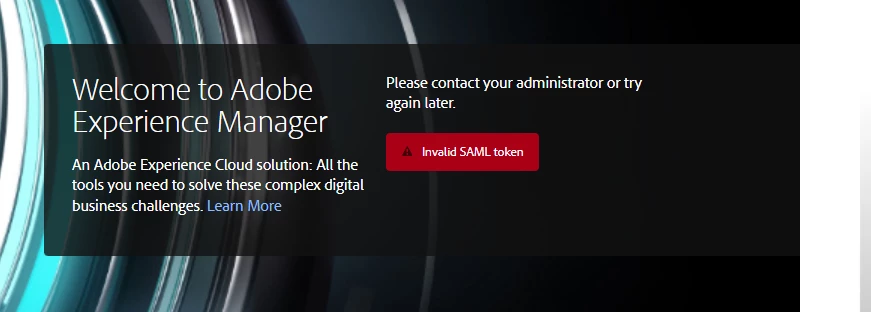
 

Thanks in advance.

Chanwalav23Accepted solution
Level 2
Apr 27, 2022 7:43 PM UTC

Issue resolved. I have got the updated certificate from our SSO team and issue resolved.

4 replies

DEBAL_DAS
New Member
Apr 25, 2022 3:56 PM UTC

Please refer this https://experienceleaguecommunities.adobe.com/t5/adobe-experience-manager/6-4-quot-invalid-saml-token-quot-error/m-p/383202


As you are facing the issue with QA environment , did you upload separate(QA environment specific) SAML certificate to AEM QA environment?

Translate
Debal Das, Senior AEM Consultant
Level 2
Apr 25, 2022 4:05 PM UTC

Hi Das,

I have gone through the above link that you shared and that didn't helped me. And yes I have updated the QA environment specific configs.


Thanks,

Vijay.

Translate
Chanwalav23AuthorAccepted solution
Level 2
Apr 27, 2022 7:43 PM UTC

Issue resolved. I have got the updated certificate from our SSO team and issue resolved.

Translate
this-that-the-otter
Level 4
Apr 7, 2025 1:44 PM UTC

We faced this issue recently and it was related to the system time being off. Syncing the system clock with NTP resolved the issue. Here's what we saw in the logs prior to updating the system clock: 


==> /apps/author/crx-quickstart/logs/error.log <== 07.04.2025 09:30:19.190 *INFO* [qtp1413716254-60] com.adobe.granite.auth.saml.SamlAuthenticationHandler Login failed. SAML token invalid. 07.04.2025 09:30:19.191 *INFO* [qtp1413716254-60] com.adobe.granite.auth.saml.SamlAuthenticationHandler SAML error with reason: invalid_token detected, redirect user to: /libs/granite/core/content/login.error.html?j_reason=invalid_token 07.04.2025 09:30:19.192 *ERROR* [qtp1413716254-60] org.apache.sling.auth.core.impl.SlingAuthenticator doLogin: Cannot login: Response already committed


Translate