Solved
Apache tika core vulnarability
Hello,
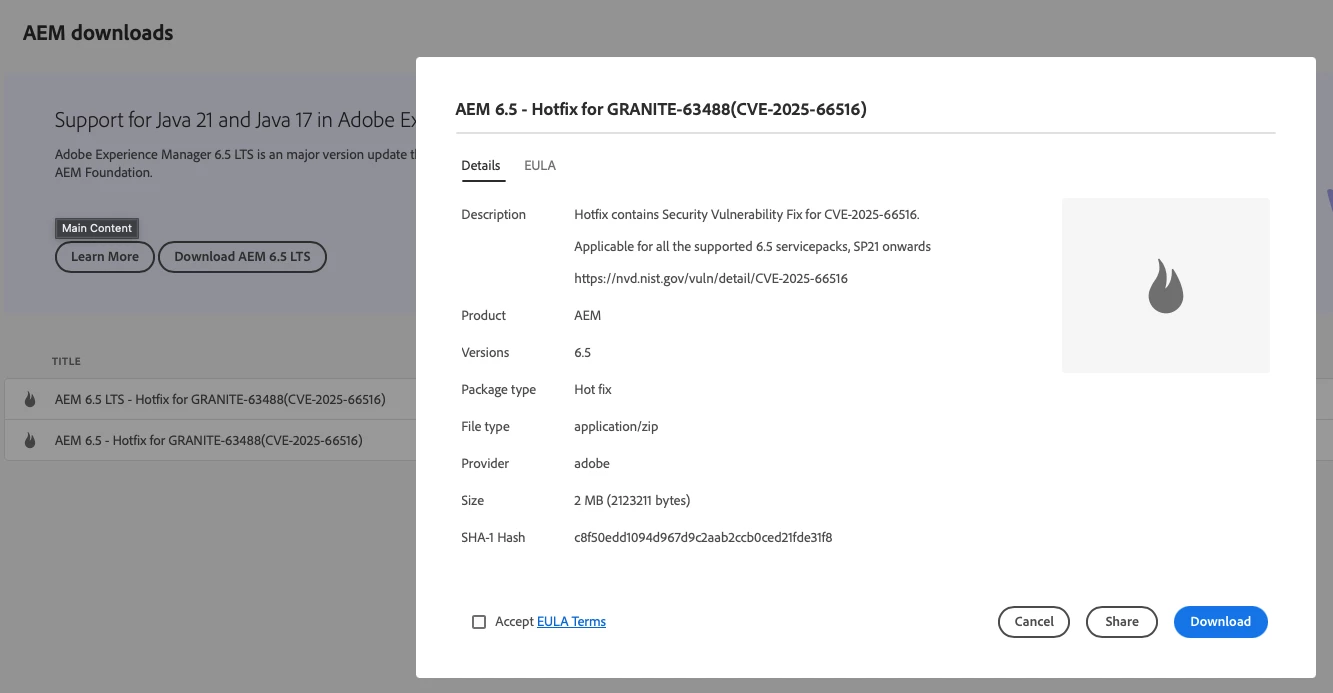
We are using AEM 6.5.22 (on premise version). which uses Apache Tika-core and Tika-parsers bundles with versions 1.28.5.
Our Infosec team has reported a vulnerability on these versions and suggested to use the versions 3.2.2 and above.
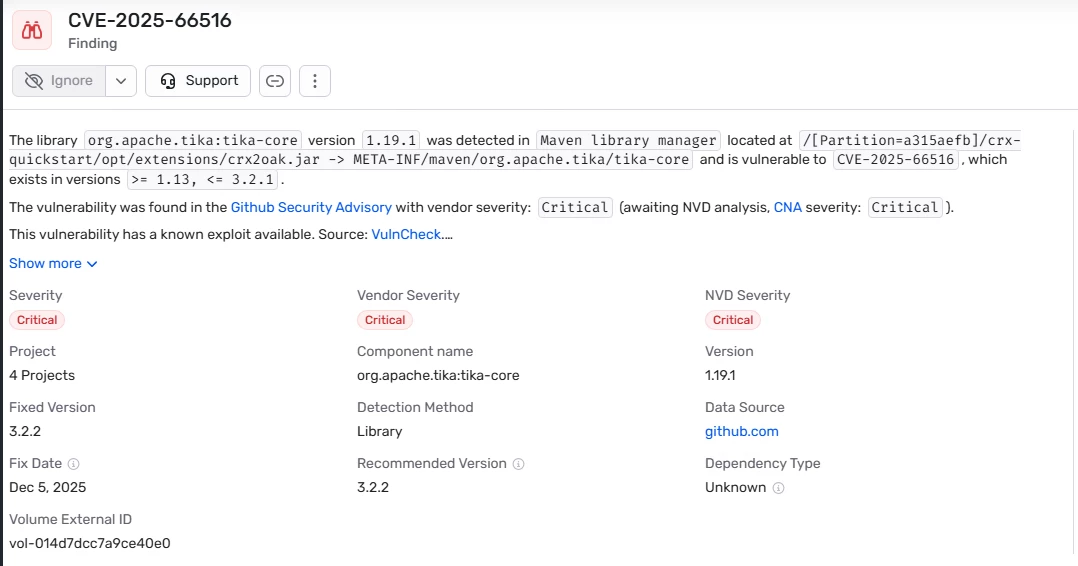
As I checked the maven repository : https://mvnrepository.com/artifact/org.apache.tika/tika-core all the versions below 3.2.2 have vulnerability.
We cannot directly updated the versions on our side as this is OOTB.
Also, when checked with the latest service pack (6.5.25) also doesn’t have latest tika-core.
Any thoughts/suggestions would be much appreciated.
Regards,
Rohit