IagoLima
Jul 15, 2024 2:10 PM UTC

Resolving Content Security Policy (CSP) after 2.4.6-p6 patch

Hi!

I'm working on moving all my JSs to have the "nonce" attached to all of them but even after handling all the cases I'm still seeing the error popping up for AdobeDTM JS as the print below shows:
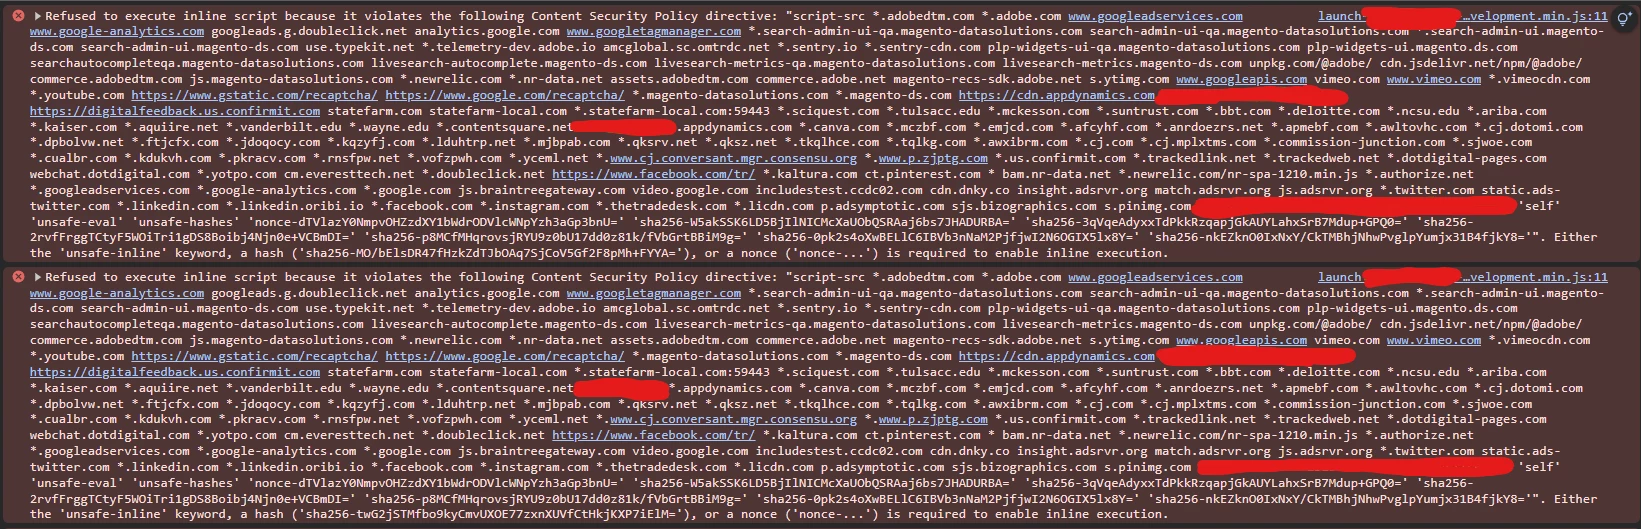
"nonce" is there inside the script tag:


But the calls keep on failing, any ideas on how to solve this? We are not willing to "allow inline script" since this is kind of the main topic of the patch itself.

This post is no longer active and is closed to new replies. Need help? Start a new post to ask your question.

2 replies

sarav_prakash
Community Advisor
Community Advisor
Jul 15, 2024 5:37 PM UTC

Your CSP policy seems to be incorrect. You are whitelisting a lot of domains + running nonce validation + running hash validation + 'unsafe-eval' + 'unsafe-hashes' 


First eval itself is completely evil. And you included `unsafe-eval`. CSP3 removed 'unsafe-eval' as recognized directive. Should remove it. 

Second, remove 'unsafe-hashes' also.


Use tools like https://csp-evaluator.withgoogle.com/ and https://cspvalidator.org/#url=https://cspvalidator.org/ to validate your policy.


If your CSP policy having bug. Guessing, removing the unsafe directives should work. Else follow the validator tools for recommended fix.

Translate
kautuk_sahni
Level 9
Jul 23, 2024 2:13 PM UTC

@iagolima Did you find the suggestion helpful? Please let us know if you require more information. Otherwise, please mark the answer as correct for posterity. If you've discovered a solution yourself, we would appreciate it if you could share it with the community. Thank you!

Translate
Kautuk Sahni